What Happened With the Linux KVM Vulnerability?
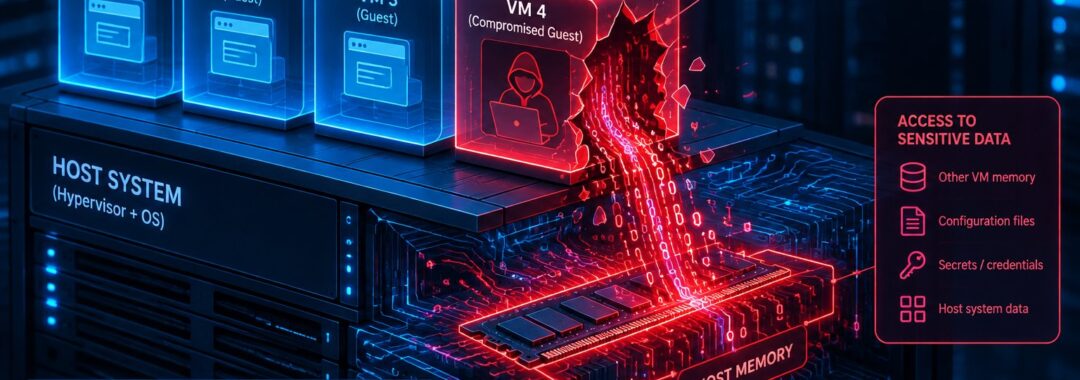
A critical Linux KVM vulnerability tracked as CVE-2026-99312 has been disclosed that allowed researchers to read approximately 127 GB of a cloud server’s memory from inside their own virtual machine on DigitalOcean. This Linux KVM vulnerability affects only hosts running AMD processors with nested virtualization enabled, according to the report.
The flaw was discovered by Oren Yomtov, a researcher at Terra Security, who reported it through the provider’s bug bounty program. The provider confirmed the exploit worked on its own hosts and treated it as critical. Linux KVM maintainers were informed on October 21 and merged a fix on November 2, with fixed kernels shipping upstream on the Tuesday before the research went public.
Source: The Hacker News — New Linux KVM Flaw CVE-2026-99312 Lets Guest VMs Access Host Memory on AMD Hosts
How Does This KVM Memory Access Attack Work?
According to Terra’s technical analysis, the vulnerability stems from a use-after-free condition involving a pointer left pointing at freed memory. KVM confines each VM using a nested page table that translates the VM’s memory addresses into the host’s real memory.
The attack chain works as follows:
- Some hosts allow a VM to run a VM of its own (nested virtualization)
- When a reset signal called INIT stops the nested VM, KVM skips restoring the outer VM’s pointer
- This leaves the pointer referencing a page of memory the kernel has already freed
- Once the kernel reuses that freed page, the guest can fill it with entries of its own choosing
- The processor follows these forged entries as if they were the legitimate table
The forged entries could name any physical page on the host, which is how approximately 127 GB of the server’s RAM became accessible to a guest that was never authorised to access it. Both tests required root access inside a VM controlled by the researchers—an attacker would need the same position.
Origin of the Vulnerability
The flaw was ironically created by a security fix. A 2022 patch for a different nested-virtualization bug (CVE-2022-3344) switched a reset path back to the outer VM’s control block but missed the page-table pointer. This error sat in the kernel for just under four years before discovery.
What Systems Are Affected?
The vulnerability specifically impacts:
- AMD-based KVM hosts with nested virtualization enabled
- Kernels from version 6.1 (2022) onwards, including 5.15.81 and 6.0.11 releases
- Distribution kernels built on affected kernel lines
Intel-based KVM hosts are not affected, as the vulnerable code exists only in KVM’s support for nested virtualization on AMD. Many cloud providers surveyed by researchers were not vulnerable because they had not enabled nested virtualization on AMD.
Current Distribution Status
As of publication, distribution kernels mostly do not have the fix:
- Debian: All releases listed as vulnerable, fix only in unstable
- Ubuntu: Rated High severity, kernels listed as vulnerable with no fixed package released
- Red Hat: Enterprise Linux 9 and 10 kernels affected with fix deferred; Enterprise Linux 8 not affected
What Is the Business Impact?
On shared servers, the exposed memory can include other customers’ virtual machines, making this a significant concern for multi-tenant cloud environments. Severity ratings for this Linux KVM vulnerability vary considerably:
- Linux kernel CVE team: 8.8 out of 10, with high impact on confidentiality, integrity, and availability
- Red Hat preliminary assessment: Moderate at 5.6, treating impact as denial-of-service only
- Cloud provider assessment: Critical for shared cloud environments
There are no reports of the flaw being used outside research, according to VirtFusion, a virtualization platform vendor tracking the issue. No exploit code has been published, and no guidance exists for detecting past exploitation attempts.
What This Means for Australian Organisations
Note: This is general guidance for Australian businesses, not a claim from the source material.
Australian organisations running their own KVM infrastructure on AMD hardware should assess their exposure promptly. This is particularly relevant for:
- Organisations subject to the SOCI Act operating critical infrastructure with virtualised environments
- Businesses with Notifiable Data Breaches obligations who may need to consider whether hosted data could have been exposed
- Organisations implementing the ACSC Essential Eight, where patching operating systems is a key mitigation strategy
A cyber security maturity assessment can help identify virtualisation risks within your environment.
Actionable Recommendations
Organisations running KVM on AMD hardware should take the following steps:
- Check nested virtualization status: Run
cat /sys/module/kvm_amd/parameters/nested— a value of 1 or Y means nested virtualization is on - Update host kernels: Fixed versions include stable kernel 7.3.5 and long-term kernels 6.18.64 and 6.12.118
- Reboot hosts: A newly installed kernel does not protect the host until reboot
- Apply interim mitigation: If patching is not immediately possible, add
options kvm_amd nested=0to the host’s module configuration and reboot - Warn tenants: If disabling nested virtualization, notify users who depend on running VMs within VMs
For ongoing protection against vulnerabilities like this, consider implementing vulnerability management services to maintain visibility across your infrastructure.
Frequently Asked Questions
What is CVE-2026-99312?
CVE-2026-99312 is a Linux KVM vulnerability that allows guest virtual machines to access host memory on AMD-based systems with nested virtualization enabled. According to researchers, it enabled reading approximately 127 GB of server memory from within a guest VM.
How can I protect my servers from this KVM vulnerability?
Update your host kernel to a fixed version (stable kernel 7.3.5 or long-term kernels 6.18.64/6.12.118) and reboot. If you cannot update immediately, disable nested virtualization by adding options kvm_amd nested=0 to your module configuration and rebooting the host.
Are Intel-based servers affected by this vulnerability?
No. According to the report, Intel-based KVM hosts are not affected because the vulnerable code exists only in KVM’s support for nested virtualization on AMD processors.
Key Takeaways
- CVE-2026-99312 affects AMD-based KVM hosts with nested virtualization enabled
- Researchers accessed approximately 127 GB of host memory from a guest VM
- The flaw originated from a 2022 security fix and went undetected for nearly four years
- Fixed kernels are available upstream but most distribution kernels remain unpatched
- Disabling nested virtualization provides interim protection
- No exploitation outside research has been reported
Conclusion
This Linux KVM vulnerability represents a significant risk for organisations running virtualised infrastructure on AMD hardware. The ability for a guest VM to access host memory—potentially including other customers’ virtual machines—underscores the importance of prompt patching and proper managed security services for virtualised environments.
If your organisation needs assistance assessing your exposure to this vulnerability or implementing appropriate mitigations, speak with our security team today.