What Happened With the Telegram Widgets Vulnerability?
A Telegram widgets vulnerability has prompted urgent warnings from security researchers after demonstrations suggested the new feature may enable remote code execution (RCE) attacks. According to Kaspersky, the flaw may have been exploited in the wild to deliver malware, raising significant concerns for the messaging platform’s vast user base just days after the widgets feature launched.
The security firm warned on November 13, 2026, that it had observed malicious activity potentially tied to the vulnerability. Users who visited certain Telegram channels may have been exposed to exploitation that resulted in malicious scripts running without their knowledge, according to the report.
Source: SecurityWeek – Telegram Widgets Hit by RCE Demos, Malware Warning Days After Launch
How Does This Telegram Attack Work?
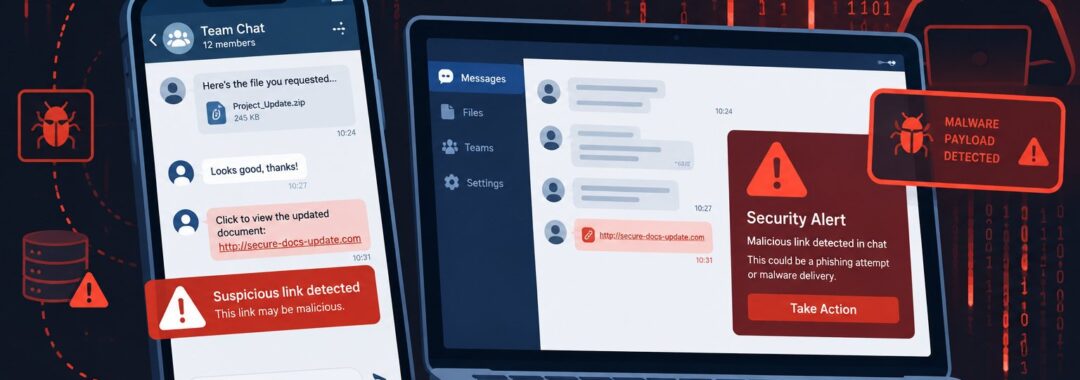
According to Kaspersky’s analysis shared on its Russian-language Telegram channel, the exploitation occurs when users visit specific Telegram channels containing malicious content. The attack chain reportedly involves:
- A PowerShell script executing without user knowledge
- The script fetching and launching WebRAT malware (also known as Salat Stealer)
- Attackers gaining control of infected systems
WebRAT is described as a Rust-based trojan capable of stealing cryptocurrency wallet data and Telegram account credentials, in addition to providing remote access to compromised systems.
RCE Demonstrations Raise Alarm
Telegram CEO Pavel Durov promoted the widgets feature on X on November 10, stating that any message on the platform could now become an app. The following day, researchers at V12 posted a video demonstrating what they described as remote code execution, showing a bot interaction causing the Calculator app to open on an Android device.
V12 later published a second video claiming to have another RCE exploit working against the supposedly patched Windows Telegram client. The researchers expressed concern that allowing QuickJS, a JavaScript engine, to run inside messages without a sandbox creates a large attack surface.
Technical Analysis of the Telegram Widgets Vulnerability
Kaspersky did not share detailed technical information about the exploitation method or disclose how many users were targeted. However, the security firm’s primary recommendation was clear: “do not launch widgets in Telegram until a fix is released.”
Telegram responded to the initial Android demonstration on the same day it was published, stating the issue “was fixed yesterday, and the fix was deployed to all users earlier today.” However, V12’s subsequent Windows exploit demonstration suggests the Telegram widgets vulnerability may have affected multiple platforms.
Durov’s Response
Pavel Durov has dismissed the severity of the reports, writing on X on November 13: “No one could be hacked just by receiving a message.” According to Durov, any attack required the user to first start a third-party service, and that scenario has since been fully patched on the server side. He challenged skeptics to hack his own account.
Business Impact of Messaging Platform Vulnerabilities
Vulnerabilities in widely-used messaging platforms pose significant risks to organisations, particularly those using such platforms for business communications. The potential for credential theft and system compromise through the Telegram widgets vulnerability demonstrates the risks associated with:
- Shadow IT and unapproved communication channels
- Cryptocurrency wallet exposure for organisations dealing in digital assets
- Account takeover leading to social engineering attacks
- Potential lateral movement within corporate environments
Organisations using Telegram for business purposes should assess their exposure and consider implementing managed security services to monitor for suspicious activity.
What This Means for Australian Organisations
Note: This is general guidance and does not reflect claims from the source material. The source does not indicate Australian users were specifically affected.
- Australian businesses should review their acceptable use policies regarding third-party messaging applications in line with the ACSC Essential Eight application control recommendations
- Organisations handling sensitive data should consider whether messaging platforms meet their security requirements under the Privacy Act and Notifiable Data Breaches scheme
- A cyber security maturity assessment can help identify gaps in third-party application controls
Actionable Recommendations
Based on the available information, organisations and individuals should consider the following steps:
- Avoid launching widgets in Telegram until official confirmation that all vulnerabilities have been addressed
- Update Telegram clients to the latest version across all platforms (Android, Windows, and others)
- Monitor accounts for suspicious activity, particularly cryptocurrency wallets linked to Telegram
- Review corporate policies on messaging application usage
- Implement endpoint protection capable of detecting PowerShell-based attacks
For comprehensive protection against emerging threats, consider engaging vulnerability management services to maintain visibility across your environment.
Frequently Asked Questions
What is WebRAT malware?
According to the report, WebRAT (also known as Salat Stealer) is a Rust-based trojan that provides attackers with control over infected systems. It can steal cryptocurrency wallet data and Telegram account credentials.
How can I protect myself from the Telegram widgets vulnerability?
Kaspersky’s main recommendation is to avoid launching widgets in Telegram until a fix is confirmed. Users should also ensure their Telegram client is updated to the latest version and monitor their accounts for suspicious activity.
Has Telegram fixed the vulnerability?
Telegram stated that the Android issue was fixed and deployed to all users. Pavel Durov claims the attack scenario has been “fully patched on the server side.” However, researchers demonstrated what they described as a working exploit against the Windows client after the initial patch, so users should remain cautious.
Key Takeaways
- Kaspersky warns the Telegram widgets vulnerability may have been exploited in the wild
- WebRAT malware can steal cryptocurrency and Telegram credentials
- Security researchers demonstrated RCE on both Android and Windows clients
- Telegram claims the issues have been patched, but caution is advised
- Users should avoid widgets until comprehensive fixes are confirmed
Conclusion
The Telegram widgets vulnerability serves as a reminder that new features can introduce unexpected security risks. While Telegram disputes the severity of the issue, the warnings from Kaspersky and demonstrations from V12 researchers warrant caution from both individual users and organisations. Until the security community reaches consensus that all related vulnerabilities have been addressed, users should heed Kaspersky’s advice to avoid the widgets feature.
If your organisation needs assistance evaluating messaging platform security or responding to potential compromises, speak with our security team at OziTechs for expert guidance.