What Happened: Google Warns Fully Automated AI Attacks Are Coming Soon
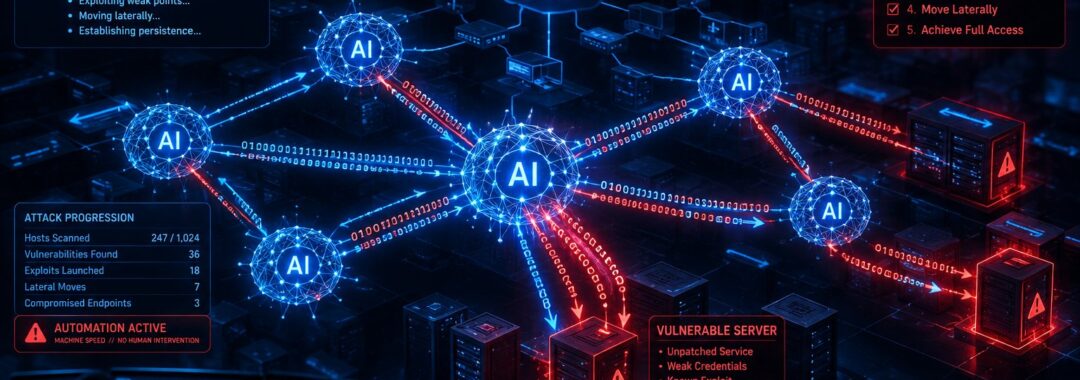
Automated AI attacks are moving from theory to practice, and Google warns that fully autonomous attacks are coming soon. According to Google’s Threat Intelligence Group (GTIG), threat actors have moved beyond experimental use of artificial intelligence and are now systematically deploying AI-powered offensive frameworks to automate vulnerability discovery and exploitation at machine speed.
The report reveals that both financially motivated cybercriminals and state-sponsored groups have adopted these techniques. GTIG researchers project that within the next three months, attackers will be capable of launching unsophisticated attacks requiring “little to no human interaction.” Even more concerning, they estimate “sophisticated, fully autonomous” agentic attacks will emerge within six months.
Source: BleepingComputer — Google warns that fully-automated AI attacks are coming soon
How Do Automated AI Attacks Work?
Attackers are now systematically abusing open-source penetration testing suites to run fully automated attacks. According to the report, the frameworks being weaponised include:
- ARTEX — An AI pentesting framework that the FBI warned has been weaponised since August 2026
- CAIRN — An open-source multi-agent penetration-testing framework
- CyberStrikeAI
- HexStrike AI
These frameworks enable adaptive attacks against internet-exposed endpoints vulnerable to low-complexity flaws. Large language models (LLMs) can easily build exploits for these vulnerabilities, removing the need for human expertise in the attack chain.
The exploit_agent Framework
GTIG discovered a particularly sophisticated system called ‘exploit_agent’ — a multi-agent system that fully automates vulnerability finding and exploitation. This framework was used in attacks targeting French media, entertainment, and education websites.
According to Google, this marks the first time GTIG identified threat actors using LLM frameworks to fully automate vulnerability discovery and exploitation “without a human in the loop.” The system analyzes software updates on popular web applications to find signs of security flaws and automatically attempts to exploit them.
Technical Analysis: Real-World Attack Examples
The report details several concerning attack campaigns demonstrating the growing sophistication of automated AI attacks:
U.S. Aerospace Sector Attack
Threat actors deployed CAIRN, the multi-agent penetration-testing framework, in an attack against the U.S. aerospace sector. This demonstrates that critical infrastructure is already being targeted by these AI-powered tools.
North Korean Claude Code Campaign
Suspected North Korean hackers have been observed using Claude Code to deliver malware. An activity cluster tracked as UNC6836, with suspected links to “Midnight Neptune,” targeted cryptocurrency firms in North America and Europe using modified Claude Code. After initial compromise, attackers modified the Claude Code app’s settings to trigger the download of the SOMBERMEME backdoor at launch.
FBI Warning on ARTEX
The FBI issued an advisory warning that multiple threat actors have weaponised the ARTEX AI pentesting framework since August 2026. Attacks have targeted organisations across financial, government, technology, defence, healthcare, and other sectors.
What Is the Business Impact of AI-Driven Cyber Attacks?
The deployment of these AI frameworks has dramatically decreased the time defenders have to patch their systems. Google warns this creates a critical window where organisations are vulnerable before patches can be applied.
Additionally, these tools are generating false leads that burden security teams. The report cites the PHP2Shell example, where hundreds of purported proof-of-concept exploits — mostly AI-generated — appeared shortly after PHP announced two security flaws. Defenders faced significant burden verifying this code and developing protections.
Beyond automated exploitation, Google reports:
- AI is now routinely used in influence operations by state-backed groups, commercial vendors, and political networks
- LLMjacking has become a widespread problem, with attackers exploiting compromised AI access at significant cost to affected organisations
What This Means for Australian Organisations
Note: The source material does not specifically mention Australian victims. The following is general guidance for Australian businesses.
Australian organisations should consider how automated AI attacks affect their security posture. Key considerations include:
- Reviewing patching timelines against the ACSC Essential Eight framework — the reduced window between vulnerability disclosure and automated exploitation makes timely patching more critical than ever
- Ensuring vulnerability management processes can respond rapidly to emerging threats
- Organisations covered by the SOCI Act should assess whether their critical infrastructure defences can detect and respond to machine-speed attacks
Actionable Recommendations
To defend against automated AI attacks, organisations should implement the following measures:
- Accelerate patch management cycles — Reduce the window between vulnerability disclosure and remediation through managed security services
- Monitor for AI-powered reconnaissance — Implement detection for automated scanning and exploitation attempts
- Harden internet-exposed endpoints — Prioritise securing public-facing systems against low-complexity vulnerabilities
- Validate proof-of-concept code — Don’t trust PoC exploits without verification, as AI-generated false leads are increasing
- Review AI tool configurations — Audit settings for any AI coding assistants to prevent supply chain compromises
Frequently Asked Questions
What are automated AI attacks?
Automated AI attacks use artificial intelligence frameworks and large language models to discover vulnerabilities and build exploits without human intervention. These attacks operate at machine speed, dramatically reducing the time between vulnerability disclosure and active exploitation.
How can organisations protect against AI-powered cyber threats?
Organisations should prioritise rapid patching of internet-exposed systems, implement continuous vulnerability monitoring, and deploy detection capabilities for automated scanning attempts. Working with a cybersecurity maturity assessment can help identify gaps in your defences.
Which industries are being targeted by AI-driven attacks?
According to the FBI advisory cited in the report, attacks using the ARTEX framework have targeted organisations in the financial, government, technology, defence, healthcare, and other sectors. The aerospace and cryptocurrency industries have also been specifically mentioned as targets.
Key Takeaways
- Google reports threat actors are now using fully automated AI attacks with no human in the loop
- Sophisticated, fully autonomous attacks are projected to emerge within six months
- Open-source frameworks including ARTEX, CAIRN, CyberStrikeAI, and HexStrike AI are being weaponised
- The FBI has warned about ARTEX attacks since August 2026 across multiple sectors
- Defenders face reduced patching windows and must contend with AI-generated false leads
Conclusion
The era of automated AI attacks has arrived, and organisations must adapt their defences accordingly. With Google projecting fully autonomous attacks within six months, the time to strengthen your security posture is now. The speed and scale of these AI-powered threats demand equally sophisticated defensive measures.
If your organisation needs assistance preparing for this new threat landscape, speak with our security team to assess your readiness against automated AI attacks.